AI Security.

Tutorials, guides and field notes from the Webocreation team.

AI Security

15 ARTICLES
AI Security · 5 min read

Broken Access Control and IDOR: The #1 Web Security Risk

Broken access control sits at the top of the OWASP Top 10 because it is everywhere and scanners rarely find it. Here is what…NOV 19, 2026
AI Security · 4 min read

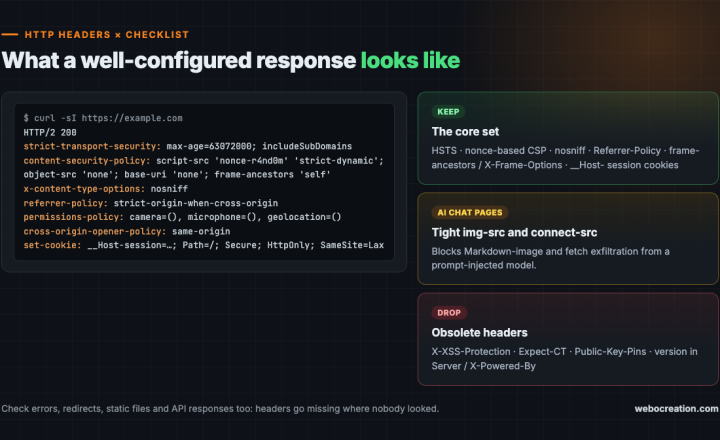
HTTP Security Headers: A Practical Checklist for 2026

A handful of response headers and cookie attributes block whole classes of attacks for almost no effort. Here are the recommended values, what each…NOV 19, 2026
AI Security · 6 min read

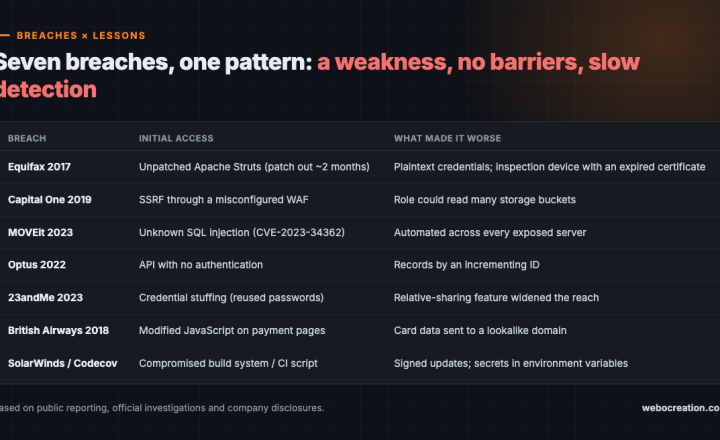
7 Real-World Breaches and the Security Lessons They Teach

Vulnerability classes feel abstract until you see what they cost. Here are seven well-documented breaches, how each one happened, and the specific controls that…NOV 19, 2026
AI Security · 5 min read

AI Code Review and Autofix: Can AI Fix Your Security Bugs?

For years defenders have been buried in findings they could not fix fast enough. AI code review and autofix promise to change that. Here…NOV 19, 2026
AI Security · 4 min read

Bug Bounty Methodology: How to Find Bugs That Get Paid

Successful bug hunters are not lucky. They read the policy, pick the right targets, understand the app deeply, and write reports that triagers love.…NOV 19, 2026
AI Security · 5 min read

How to Secure AI Agents: Design for a Compromised Model

If prompt injection cannot be prevented, how do you ship AI agents safely? The answer is the same one we used for SQL injection…NOV 19, 2026
AI Security · 5 min read

Prompt Injection Explained: How Attackers Hijack LLM Apps

Language models cannot reliably tell instructions from data. That single fact powers prompt injection, the number one risk in LLM applications. Here is how…NOV 19, 2026
AI Security · 5 min read

How AI Is Changing Offensive Security (and What Defenders Must Do)

AI is speeding up every stage of offensive security, from reading code to writing exploits. Here is what AI-assisted testing really does well, where…NOV 19, 2026
AI Security · 4 min read

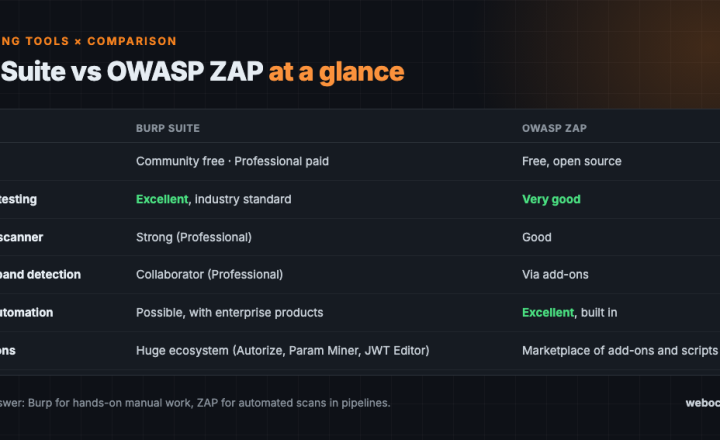
Burp Suite vs OWASP ZAP: Which Web Testing Proxy Should You Use?

An intercepting proxy is the center of every web security test. Here is how Burp Suite and OWASP ZAP compare, which features matter most,…NOV 19, 2026
AI Security · 5 min read

Software Supply Chain Security: From Log4Shell to Slopsquatting

Most of the code you ship was written by people you have never met. Here is how attackers target dependencies, build pipelines, and now…NOV 19, 2026
AI Security · 5 min read

API Security: JWT, OAuth, and GraphQL Mistakes to Avoid

APIs hand attackers your business logic with the UI stripped away. These are the JWT, OAuth, GraphQL, and REST mistakes that show up again…NOV 19, 2026
AI Security · 4 min read

SSRF Explained: From URL Previews to Cloud Credentials

A harmless-looking "fetch this URL" feature can hand attackers your cloud credentials. Here is how server-side request forgery works, why simple filters fail, and…NOV 19, 2026
AI Security · 4 min read

XSS Prevention: A Practical Guide for Modern Frameworks

Modern frameworks escape output by default, yet cross-site scripting keeps showing up. The bugs have moved to escape hatches, DOM sinks, and now AI-generated…NOV 19, 2026
AI Security · 5 min read

SQL Injection in 2026: Why an Old Bug Still Breaks Systems

SQL injection is more than 25 years old, yet it powered one of the largest data theft campaigns of the decade. Here is how…NOV 19, 2026
AI Security · 5 min read

Why Web Security Still Matters in the Age of AI

Every few years someone declares web security solved. Every year the breach reports say otherwise. Here is why the seams between components, and now…NOV 19, 2026