API Security: JWT, OAuth, and GraphQL Mistakes to Avoid
APIs hand attackers your business logic with the UI stripped away. These are the JWT, OAuth, GraphQL, and REST mistakes that show up again and again, and the fixes for each.
 Rupak NepaliPublished Nov 19, 2026
A web page hides things. An API does not. Every endpoint your mobile app or single-page front end calls is available to anyone with a proxy and some curiosity, minus the buttons, validation, and disabled fields that made it look safe.
That is why the OWASP API Security Top 10 is dominated by authorization problems, and why APIs are now where many of the most serious web bugs are found. Here are the mistakes that come up again and again.
Step zero: you cannot secure what you have not mapped
Testing (and defending) starts with an inventory. Endpoints surface through OpenAPI or Swagger files, JavaScript bundles, mobile app traffic, and plain fuzzing. Watch especially for old versions: if /api/v3/users checks permissions properly, does /api/v1/users still exist, and does it?
Forgotten test and legacy endpoints are a recurring breach pattern. Continuous discovery of your own APIs is not optional.
REST: authorization, data exposure, and mass assignment
The big three for REST APIs:
- Broken object level authorization (BOLA). Change the ID in the request and you get someone else’s record. Every object fetch needs an ownership check.
- Excessive data exposure. The API returns the full user object (password hash, internal flags, other people’s emails) and trusts the front end to hide it. Return only the fields each client needs.
- Mass assignment. The endpoint binds the entire request body to a model, so extra fields like
"is_admin": trueget saved. Use explicit input schemas.
Also test type confusion: what happens when an ID is sent as an array, a string, a negative number, or an object instead of an integer?
JWT pitfalls
JSON Web Tokens are everywhere, and their flexibility is the problem. Common failures:
alg: none. Libraries that accept unsigned tokens let anyone forge one.- Algorithm confusion. A server expecting RS256 (asymmetric) is tricked into verifying with HS256, using the public key as an HMAC secret, which the attacker also has.
- Weak secrets. HMAC keys like
secretor a company name can be brute-forced offline from a single token. - Header injection. Fields like
kid,jku, andx5ucan point verification at attacker-controlled keys if they are trusted blindly. - Missing claim checks. Not validating
exp,iss, andaudmeans expired tokens or tokens for a different service still work.
The fix is consistent: pin the expected algorithm in your verification code, use strong keys, ignore key-location headers unless you control them, and validate every claim.
# Pin the algorithm and validate claims explicitly
jwt.decode(token, PUBLIC_KEY, algorithms=["RS256"],
           audience="api.example.com", issuer="https://auth.example.com")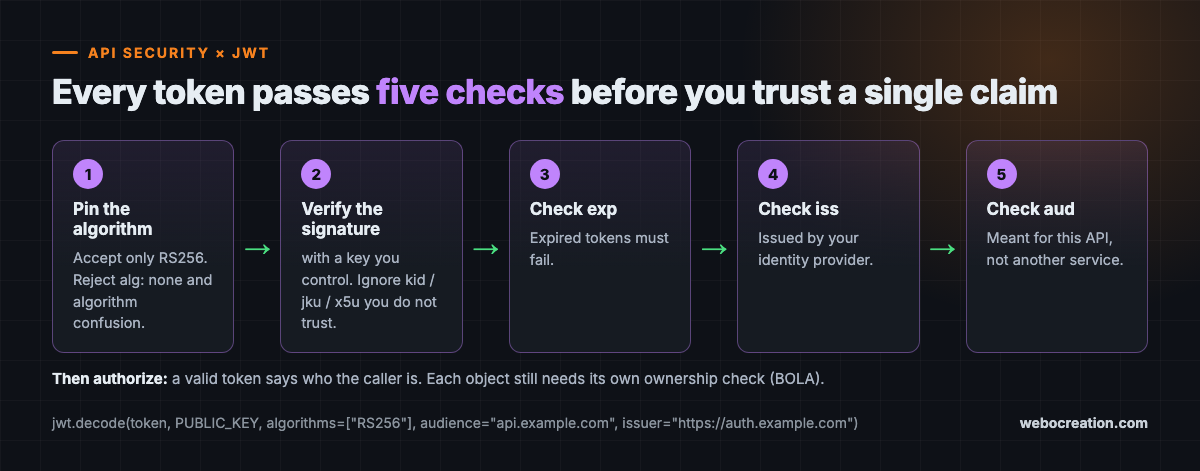
OAuth and OpenID Connect
OAuth bugs often lead to full account takeover. The safe baseline is:
- Use the authorization code flow with PKCE for every client, including web apps. PKCE stops intercepted authorization codes from being redeemed by someone else.
- Match redirect URIs exactly. Prefix or wildcard matching, combined with an open redirect anywhere on your domain, lets attackers steal codes or tokens.
- Validate the
stateparameter to prevent login CSRF. - Avoid the old implicit flow, which puts tokens in the URL.
GraphQL-specific risks
GraphQL gives clients enormous flexibility, which creates its own problems:
- Introspection exposure. Introspection reveals the whole schema. Disabling it in production helps, but it is not a complete defense, because field suggestions and client bundles leak the same information.
- Resolver-level authorization gaps. Checking permissions on the top-level query is not enough. Every resolver that returns sensitive data needs its own check, because nested queries can reach objects by a different path.
- Resource exhaustion. Deeply nested or very wide queries can take down a server. Enforce depth and complexity limits.
- Batching and aliases. A single request can contain hundreds of aliased login attempts, sailing past request-based rate limits.
Rate limits should count business operations
That last point generalizes. Rate limits that count HTTP requests are easy to bypass with batching, aliases, and many IPs. Limit the business operation instead: password attempts per account, OTP checks per session, gift card redemptions per user.
Treat third-party data as untrusted
Finally, data your API receives from other APIs (partners, webhooks, and increasingly LLM outputs) is input like any other. Validate it, encode it, and never pass it straight into a query or a renderer.
Practice on intentionally vulnerable APIs such as crAPI, VAmPI, or Damn Vulnerable GraphQL Application, not on production systems you are not authorized to test.
Key takeaways
- Map every API, including old versions and forgotten endpoints.
- BOLA, excessive data exposure, and mass assignment dominate REST API flaws.
- Pin JWT algorithms, use strong keys, and validate every claim.
- Use OAuth’s authorization code flow with PKCE, exact redirect matching, and
state. - GraphQL needs resolver-level authorization plus depth, complexity, and batching limits.
Go deeper with the book
This article is adapted from Web Security in the Age of AI: Attacks, Defenses, Tools, and Bug Hunting for Modern Web Applications and LLM Systems by Rupak (see Chapter 12, “API Security: REST, GraphQL, JWT, and OAuth”).
The book pairs every attack with its fix across 27 chapters, from core vulnerabilities and professional tools to bug bounty hunting, attacking and defending LLM applications, and lessons from real breaches. It includes hands-on labs, review questions, a full testing checklist, a security headers reference, and an LLM red teaming playbook.
Related reading
- Broken Access Control and IDOR: The #1 Web Security Risk
- Bug Bounty Methodology: How to Find Bugs That Get Paid

Rupak Nepali is a web developer, manage Webocreation website and the author of six books:
Getting Started with OpenCart Module Development (Packt, 2013),
OpenCart Theme and Module Development (Packt, 2015),
OpenCart 4: Dev Guide for Themes & Extensions (2024),
OpenCart 4: User Manual (2025),
Cloudflare for the Enterprise Website (2026) and
The Technical Web Guide for Marketers (2026).
Rupak has built OpenCart stores and extensions since 2010, has published more than 600 tutorials on Webocreation, and shares free OpenCart extensions on GitHub.
Find Rupak on
GitHub | Amazon | LinkedIn | X | YouTube.